Northgrid Gains 10x Core Network Visibility with NGNTA
How a regional ISP moved from reactive, complaint-driven troubleshooting to automatically detecting and blocking large-scale scanning campaigns across its core network.
Skip ahead: Challenge | Solution | Results
About Northgrid
Northgrid is a regional internet service provider serving more than 200,000 residential and business subscribers across a multi-state footprint, operating its core network from a handful of regional aggregation data centers.
Northgrid's Network Operations Center (NOC) is responsible for keeping peering links, aggregation routers, and subscriber-facing services healthy around the clock — but as automated bot and scanning traffic climbed year over year, the team's flow-sampling tools struggled to distinguish real threats from background noise at multi-gigabit scale.
CHALLENGE: Attacks Discovered by Customers, Not by the NOC
Northgrid's existing flow-sampling tools worked on averages, not individual sessions — fine for capacity planning, but nearly useless for spotting a reconnaissance sweep hiding inside legitimate-looking traffic. Port scans and credential-stuffing attempts against subscriber-facing services routinely blended into normal background noise.
More than once, the NOC learned about an active scanning campaign only after a wave of subscriber complaints about slow service — hours after the traffic pattern first appeared on the network.
"Sampled flow data told us bandwidth was up, but not why. We'd get a support ticket spike, dig through logs for an hour, and eventually find a scan that had been running since the night before. We were always a step behind."
With links running well into double-digit gigabits, Northgrid needed full-fidelity visibility that could keep up with core traffic volumes without adding inline hardware or risking packet loss on production links.
SOLUTION: Full-Fidelity Visibility at Core Network Scale
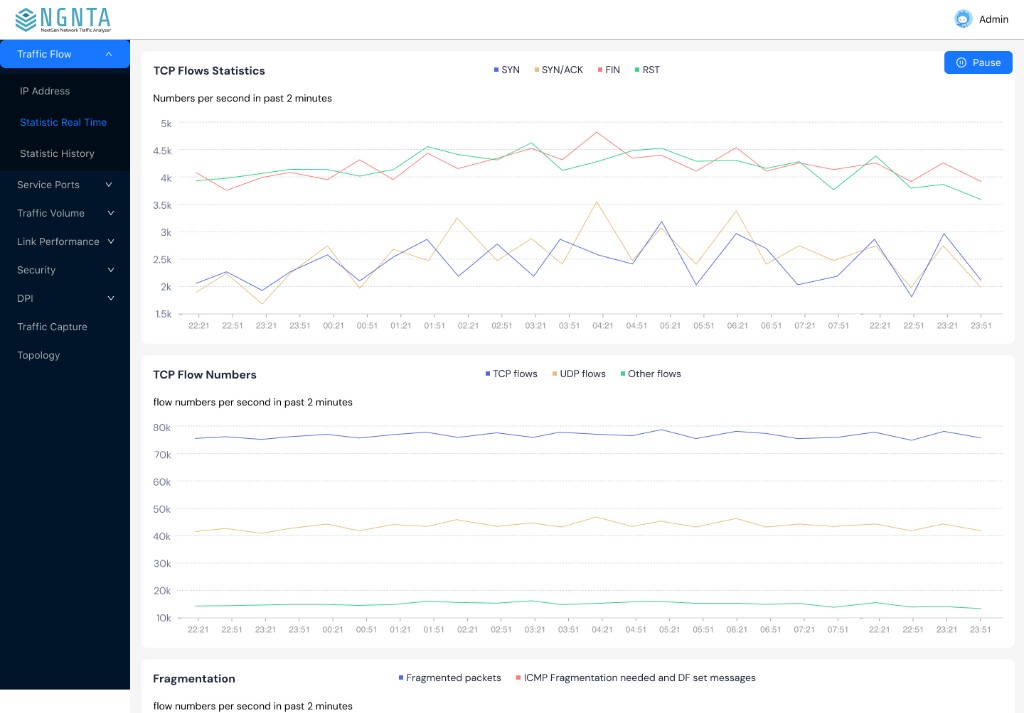
Northgrid deployed NGNTA Enterprise at its core aggregation points, with multi-link aggregation supporting well over 100 Gbps of monitored throughput — decoding every flow at line rate via passive taps, with no inline hardware in the traffic path.
NGNTA's AI-driven behavioral models, tuned with custom threat-intelligence feeds for ISP-scale traffic, now flag port scans, reconnaissance sweeps, and weak-protocol abuse the moment they start — and automated mitigation playbooks push blocks directly to Northgrid's existing routers without a NOC engineer in the loop.
"We finally have per-flow visibility at the speeds we actually run at. NGNTA doesn't just tell us bandwidth is up — it tells us exactly which IPs are doing what, in real time, at full line rate."
"The mitigation playbooks were the real unlock," Nair added. "We defined the response once, and now the system handles routine scanning the moment it starts — our team only gets paged for the stuff that actually needs a human."
RESULTS: 10x Visibility and a Quieter NOC
Northgrid now sees roughly 10x more of its network in usable detail — every flow, protocol, and anomaly across its core, versus the sampled snapshots its previous tools produced.
In its first quarter with NGNTA live, the platform automatically identified and flagged over 268,000 suspicious IPs participating in a large-scale, distributed port-scanning campaign against Northgrid's subscriber-facing infrastructure — and triggered mitigation before subscribers noticed any degradation.
Automated detection and mitigation cut NOC escalations tied to scanning and abuse traffic by roughly 40%, freeing engineers to focus on capacity planning and service quality instead of chasing alerts after the fact.
"We used to find out about attacks from angry customers. Now we get ahead of it — the system catches it, blocks it, and logs it before anyone downstream even notices a blip."
With full visibility across its core, Northgrid has also improved its ability to meet customer-facing uptime SLAs — spotting and resolving link-level issues before they escalate into service-affecting incidents.
About NGNTA
NGNTA is the trusted standard in real-time network traffic analysis and threat response, used by finance, telecom, and healthcare security teams to protect infrastructure without slowing it down. Our passive platform combines live flow analysis, AI-driven threat detection, automated mitigation, and compliance-ready audit trails in a single console.
Deployable via a single tap or mirror port with no inline hardware and no downtime, NGNTA scales from a single branch office to global critical infrastructure. Ready to see what it can do for your network?
Request a Demo